The certificate is the start,
not the finish line.

Checkpoints, evidence and deadlines for ISO 27001, ISO 9001, NIS2, DORA, SOC 2, BSI C5 and the GDPR in one place. Every piece of evidence has an expiry date and speaks up before the auditor finds it. And where there is no certificate at all — NIS2, DORA, GDPR — only what you can evidence continuously counts anyway.

Fourteen days, no payment details.
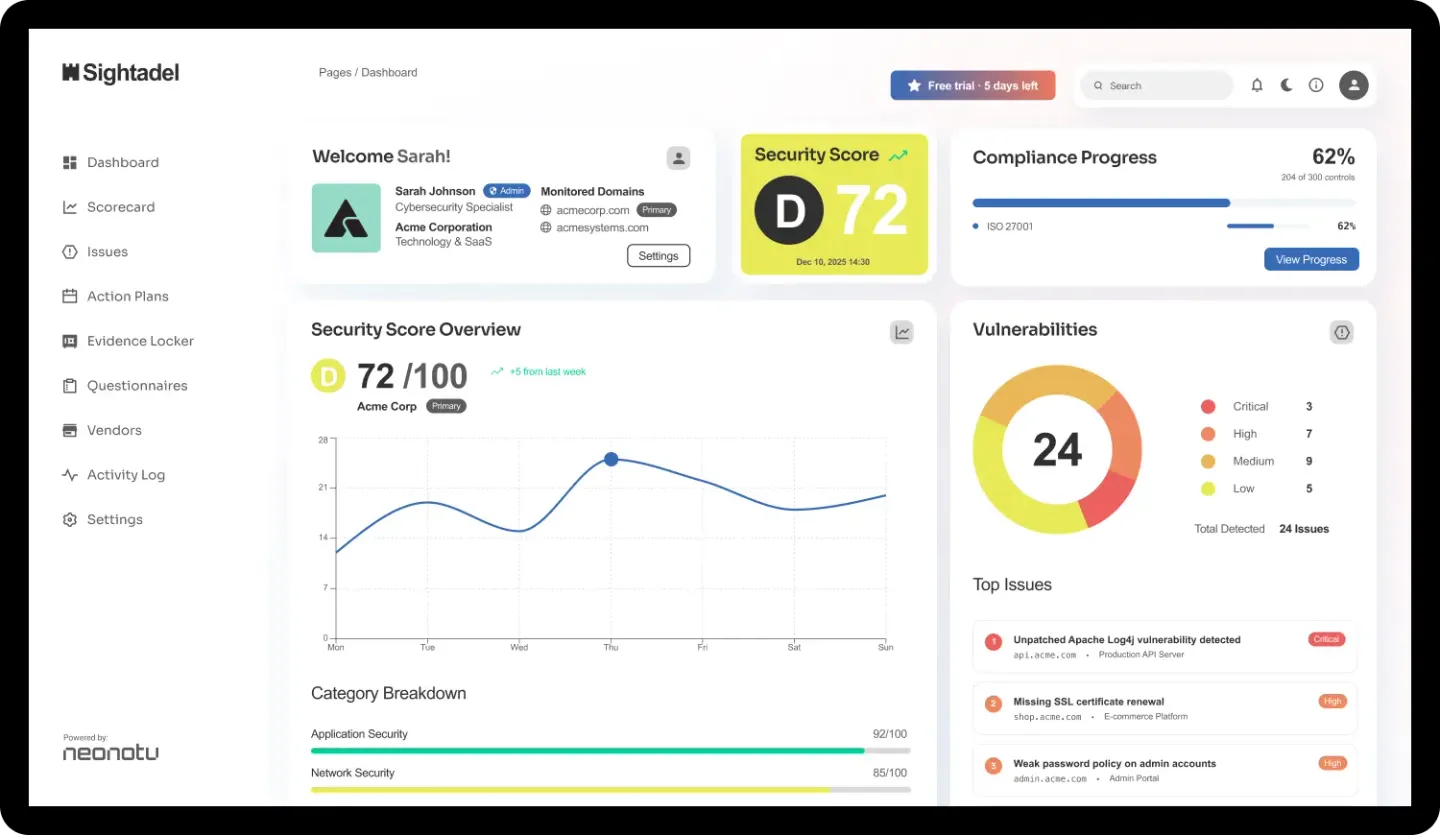
Sightadel dashboard preview
  • ISO 27001
  • ISO 9001
  • NIS2
  • DORA
  • SOC 2
  • NIST CSF 2.0
  • BSI C5
  • GDPR
  • ISO 42001
  • HACCP
  • and more
  • Hosted in Germany
  • Built in Germany
  • Article 28 processing agreement
  • Auditor access included

Built and hosted in Germany!neonotu GmbH · Sightadel

A compliance platform for ISO 27001, NIS2, DORA and seven further frameworks

Sightadel brings together in one place what is usually scattered: which requirement applies, who owns it, which evidence supports it and when it falls due again.

The difference from a spreadsheet shows up not on day one but in month eleven — when someone asks when access rights were last reviewed, and the answer does not have to come from memory.

What changes

The work does not disappear. The hunting for it does.

Today

  • Status lives in four spreadsheets, evidence in three mailboxes.
  • With the second framework the same evidence is maintained twice.
  • "When was this last reviewed?" is a question nobody answers from memory.
  • Three weeks of collating before the audit, year after year.
  • Evidence folders go to the auditor by email.

With Sightadel

  • Requirement, owner, evidence and deadline sit in one place.
  • One piece of evidence attaches to every framework that asks for it.
  • Every piece of evidence carries an expiry date and speaks up by itself.
  • Audit preparation is whatever accumulated over the year anyway.
  • The auditor gets their own read-only access.

Understand where you stand

See at a glance where the largest gaps are — and which of them actually move the needle.

  • Maturity per theme rather than one headline number that decides nothing.
  • Spot gaps before they turn into audit findings.
  • A view you can put in front of the board without translating it first.
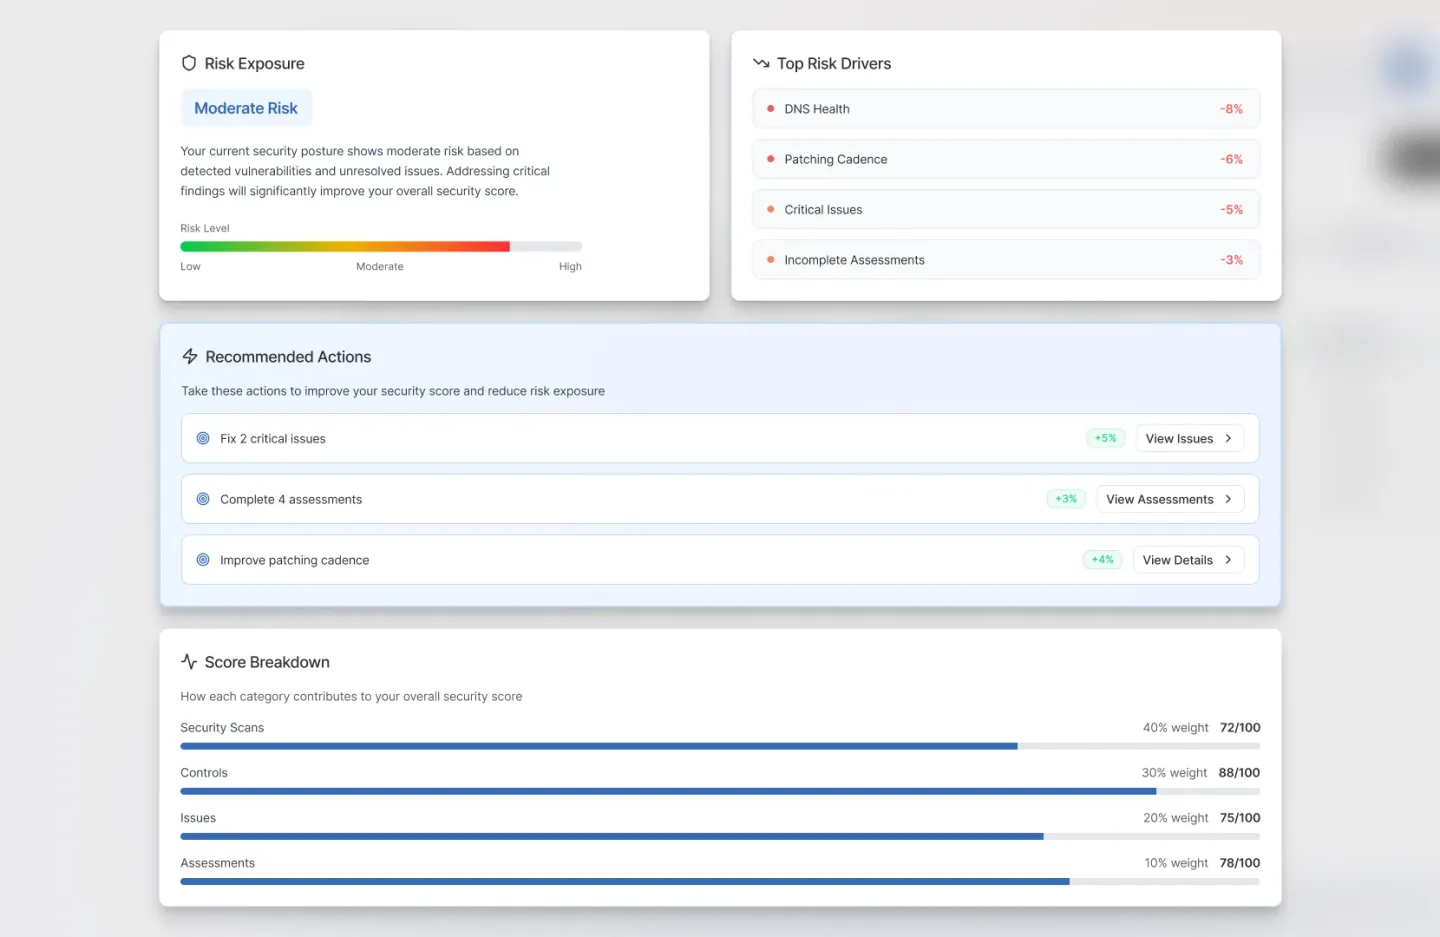
Security posture overview with maturity per theme
Maturity per themeGaps visible at onceOne view for the board

Fix what matters first

Tasks are sorted by impact, not by arrival date. So your team always knows what comes next and why.

  • Open items with deadline, owner and evidence.
  • Dependencies between tasks, risks and controls made visible.
  • Work through it in order instead of losing it across tickets and tools.
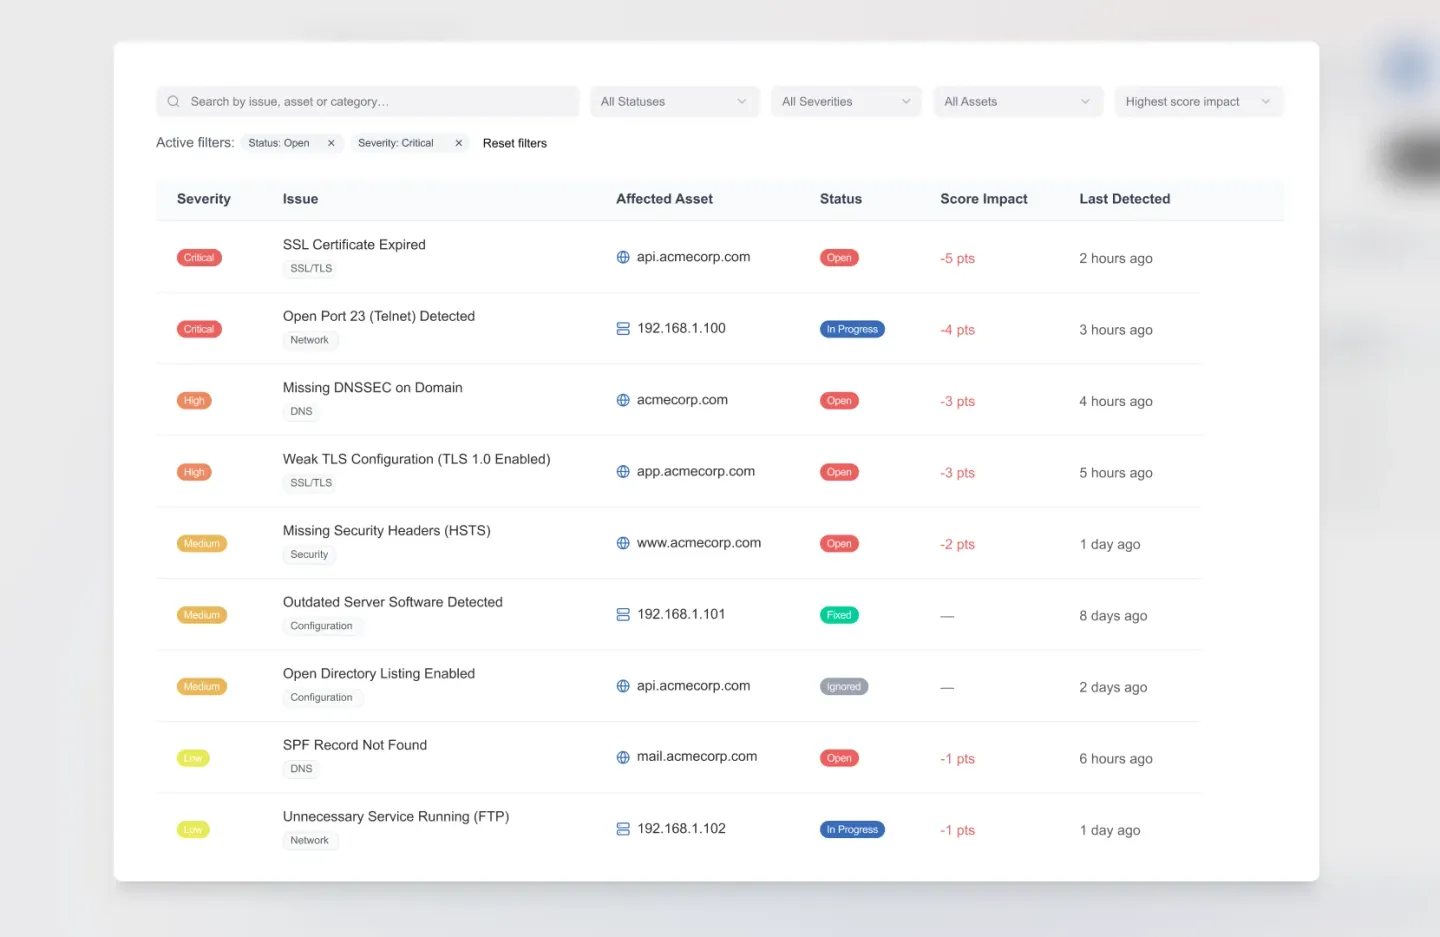
List of open items with priority, deadline and owner
Sorted by impactDeadline and ownerEvidence right beside it

On track all year

Eleven months sit between the first audit and the first surveillance audit. Whatever does not run in that time is missing later — visibly, because evidence carries a date.

  • Every piece of evidence gets an expiry date and speaks up by itself.
  • Access reviews, vendor assessments, training and restore tests run as cycles.
  • The auditor gets their own read-only access.
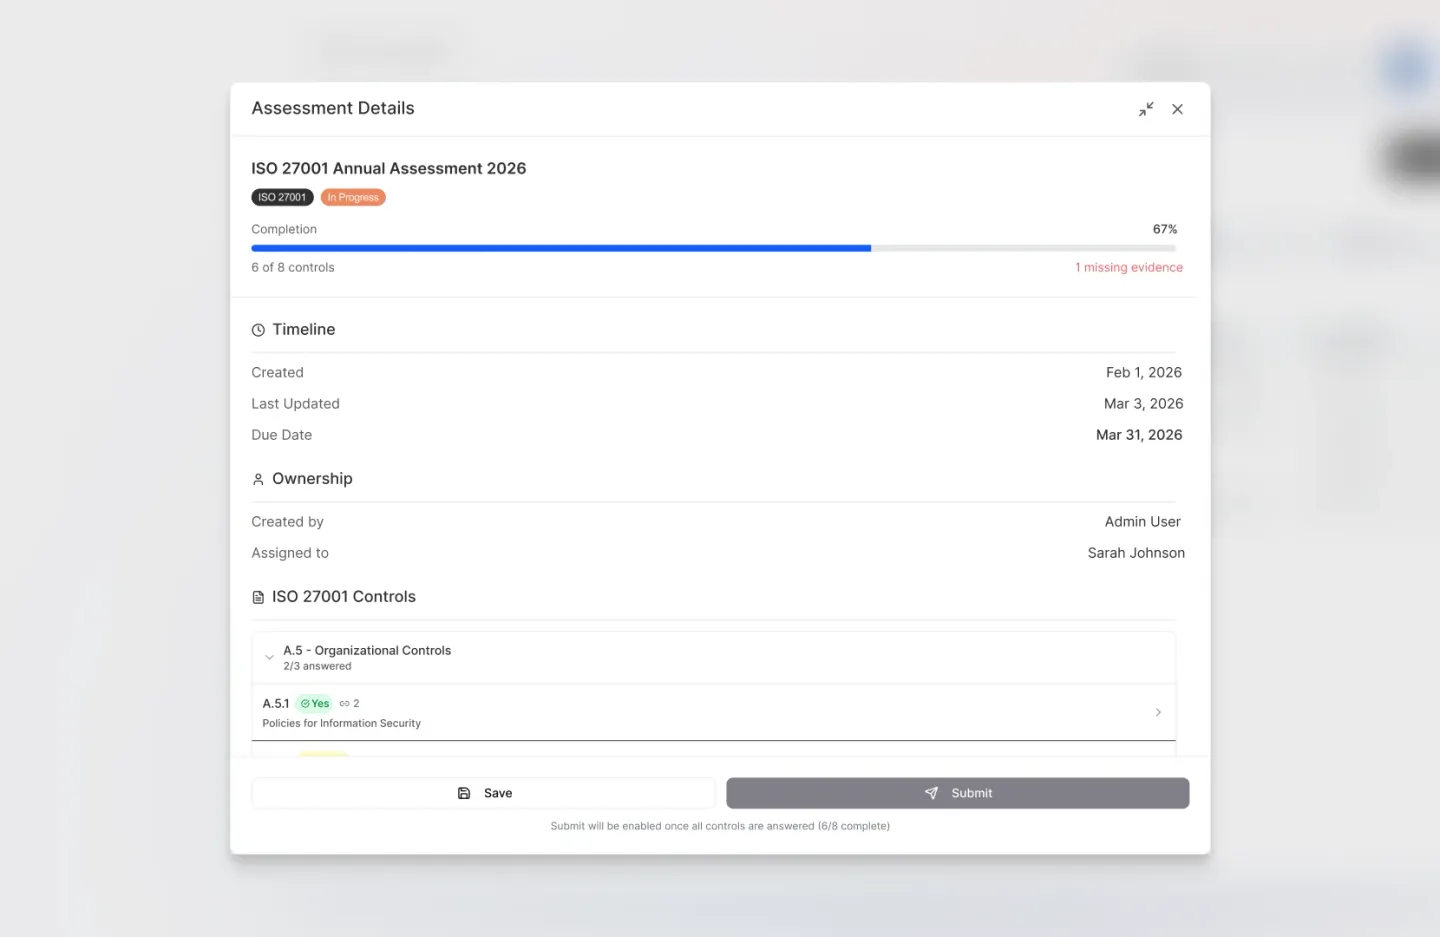
Asset monitoring with review dates and reminders
Expiry date per evidenceA reminder, not a memoryThe auditor reads, never edits

What is covered — and what you actually end up with

Not every framework ends in a certificate. That difference decides who you demonstrate compliance to and what you can show a customer.

FrameworkTypeWhat you end up with
ISO/IEC 27001CertificationCertificate from an accredited certification body, three-year cycle
ISO 9001CertificationCertificate from an accredited certification body, three-year cycle
ISO/IEC 42001CertificationCertificate for the AI management system, structured like ISO 27001
SOC 2Attestation reportReport by a CPA firm, Type I at a point in time or Type II over a period
BSI C5AttestationAuditor attestation under ISAE 3000, at a point in time or over a period
NIS2Statutory dutyNo certificate. Evidence to the supervisor, notifications after 24 and 72 hours and one month, management approval
DORAEU regulationNo certificate. Evidence to the supervisor, register of information, testing programme
GDPREU regulationNo certificate. Accountability, records of processing, technical and organisational measures
NIST CSF 2.0FrameworkNo attestation foreseen. A language for presenting maturity to management, the board and insurers
HACCPEU regulationNo certificate of its own. HACCP-based procedures under Regulation (EC) No 852/2004, checked by the food control authority
Custom frameworkBuilt by youGroup policies, contractual customer requirements, industry standards without a ready-made module

One piece of evidence, several frameworks

The same fact is asked for by several frameworks. Access management appears in ISO 27001 Annex A, in NIS2 measure 9, in DORA's ICT risk management and in the SOC 2 common criteria — the same question four times.

  • Evidence is filed once and attached to every requirement it serves.
  • When it changes, it changes everywhere. When it expires, it expires everywhere.
  • We also say what does not carry over: the NIS2 and DORA reporting deadlines are not identical, and the DORA register of information has no ISO 27001 counterpart.
  • We deliberately quote no percentage. Anyone claiming two frameworks overlap by 80 per cent has not seen your scope.

What sets us apart from the large vendors

Not everything, honestly. But these four points decide procurement time and again.

01

European frameworks are not an add-on

With vendors of SOC 2 origin, NIS2, DORA and BSI C5 are retrofitted. Here they are modules of their own with their own evidence trail — reporting deadlines and register of information included.

02

Built and hosted in Germany

Operated with creoline, support here as well. No detour through data centres elsewhere, no access under foreign law — and one question fewer in the vendor questionnaire.

03

We do not certify

You choose your certification body freely or from our partner network. Under ISO/IEC 17021 a body may not both consult and certify; that separation protects your certificate from challenge.

04

Roles that separate inside from outside

Six roles, including a read-only auditor access that is always external, and a separate role for advisors you bring in. An audit has to show who examined and who contributed.

What it costs

Licensing is per framework. That sounds more expensive than an all-in subscription but usually is not: you pay for what you actually run. If you only have to demonstrate NIS2, you are not paying for ISO 27001 as well.

Entry prices, net, in the Basic edition: BSI C5 and GDPR from €2.400 a year, ISO 9001 from €3.800, NIS2, DORA and SOC 2 from €4.500, ISO 27001 from €9.000. If ISO 27001 or ISO 9001 is part of the package, every further framework costs a permanent 5 % less. A one-year term takes another 5 % off.

Worked example

Service provider, 60 employees. ISO 9001 for customers, NIS2 because of sector and size, the GDPR anyway. Basic edition, one-year term. ISO 9001 is part of the package — which is why the discount applies to the other two.

ISO 9001, annual price€3.800,00
NIS2, annual price€4.500,00
GDPR, annual price€2.400,00
Further frameworks, −5 % on NIS2 and GDPR−€345,00
One-year term, −5 %−€517,75
Total year 1, net€9.837,25
€820a month on average — for three frameworks

The one-year term is charged once a year. Paid monthly instead, it comes to €862,92 a month, without the term discount.

Basic means five internal users and 1 GB of evidence storage. If you need more, the Professional edition comes to €12.788,42 in the first year.

See the full price list

All prices net, excluding VAT. Certification body fees come separately — they have to bill independently.

Working material you can use without us

We publish the working materials we use ourselves. If you get on fine with them and never need us again, keep them.

01

Checklists and evidence packs

ISO 27001 with all 93 controls and 28 clause checkpoints, NIS2 with 40 checkpoints, DORA with 50 requirements — as an Excel workbook and PDF.

02

Incident reporting templates

Early warning after 24 hours, notification after 72 hours, final report after one month, plus the immediate actions for the first two hours.

03

Guides

ISO 9001 in three months, the evidence pack for German medical practices and the white paper on why compliance breaks down in spreadsheets.

Frequent questions

For organisations that have to demonstrate at least one framework and find that a spreadsheet no longer does the job — typically once a second framework arrives or the first surveillance audit is due.

Start with one framework

Fourteen days of trial access, no payment details. Bring your existing spreadsheet — that is where the difference shows fastest.